Securing government services in the age of AI
Oleh Fortinet
Fortinet’s Jack Chan explains how agencies can apply Zero Trust to AI agents, protect sensitive data and use AI to strengthen threat detection as public services become more autonomous.
-1793611094078.jpg)
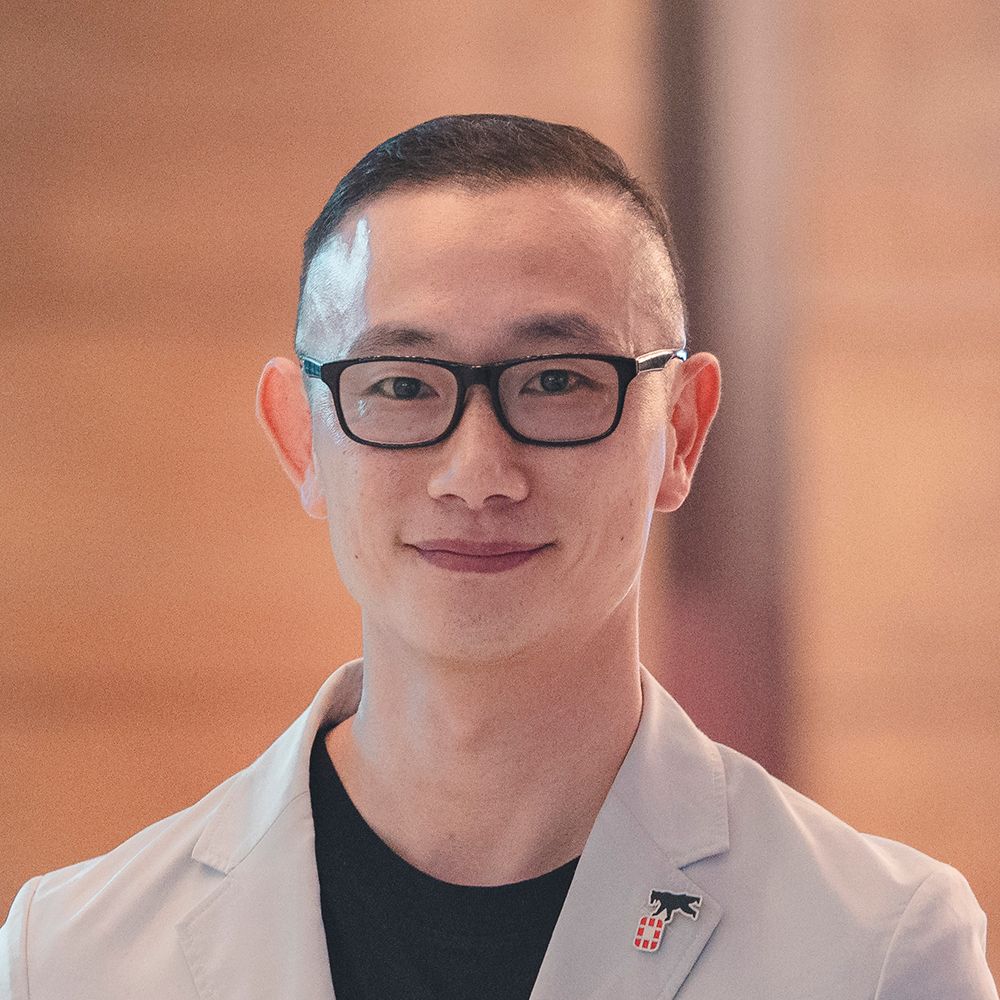
Jack Chan, Global Vice President of Product Management and Field Chief Technology Officer for Asia Pacific at Fortinet, discusses how organisations can manage AI risk, resilience and trust as autonomous systems gain greater access and authority. Image: GovInsider
A user asks a banking AI assistant for 10 sample customer records, claiming they are needed for a customer relationship management (CRM) update.
In the unprotected version of the system, the agent returns sensitive customer information from its backend database. But with security controls in place, the request is blocked.
The demonstration, shown to GovInsider during an interview with Fortinet’s Jack Chan, illustrated the risks of connecting AI agents to sensitive information.
Chan is the company’s Global Vice President of Product Management and Field Chief Technology Officer for Asia Pacific.
As expectations grow for AI agents including ability to retrieve and update records stored in databases, agencies need to consider how those capabilities could be misused, he says.
Chan explored these challenges in his GovWare 2026 presentation, Staying Ahead of Autonomy: Defending AI While AI Defends You, on October 13. He also joined the panel, The Future of Cybersecurity: Navigating Risk, Resilience, and Trust in the Digital Age, the following day.
Speaking to GovInsider after the two sessions, he explains how governments can translate AI governance into controls over an agent’s identity, access and activity.
Guardrails around the model
The banking example shows how a seemingly routine request can be used to obtain protected information.
Chan discusses prompt injection, where instructions redirect an AI system away from its intended behaviour.
He also demonstrates abusive requests that try to elicit inappropriate responses.
These risks become more consequential for the public sector when an agent can access citizen records or interact with service delivery systems.
Chan describes protections that inspect requests before they reach a large language model (LLM), check its responses, and flag or block suspected violations.
Logs allow security teams to examine the inputs and outputs involved, and reasons why malicious requests are blocked.
The aim is to “analyse the input, sanitise the output”, he explains.
Fortinet’s FortiAIGate exemplifies this approach. The product sits between AI applications and models, with controls designed to detect prompt injection, data leakage and other AI security risks.
Giving agents an owner and an end date
Those safeguards sit within a wider question of how agencies govern the agent itself.
On what Zero Trust means for AI agents, Chan describes a life cycle that begins with identifying a human owner and authenticating the agent before it accesses systems.
“The agent should also authenticate,” he says, comparing this with an employee logging into a corporate environment.
Agencies need controls over which data the agent can access and how that information is used. Agents should be granted only the minimum access required for a specific task, with that access continuously monitored and reviewed.
Chan says this should be governed by a threat model that considers the agent’s capabilities, its data sensitivity, and where that data is hosted.
Human oversight, or “human in the loop”, remains important, he adds.
Security teams must be able to revoke an agent’s authority immediately if a problem arises, and remove its access when the application is retired.
Chan also emphasises the need to govern non-human identities.
The teams maintaining government systems need tools to monitor these identities and intervene when their access is misused.
During the panel, Chan addressed agent governance, urging organisations developing their own agents or using those supplied by vendors to question their threat models.
Following government data beyond the agency
Chan says that data governance will become increasingly important as governments develop more services around AI agents.
An agent helping a citizen access a health or financial service may handle sensitive information.
Chan links this to data sovereignty.
Even when agencies use managed services or vendor platforms, they need to understand which providers process that information, where it is stored, who can access it and which jurisdiction applies.
Computing constraints can complicate these decisions.
Based on his work with customers, he says the cost of running AI internally can push organisations towards external models and services.
This creates more work in understanding and controlling how data moves outside the organisation.
Chan points to data masking as one safeguard when using external AI services: sensitive personal information should be obscured before it is passed to a model.
He also sees a gap between the pace of business transformation and the capability of security teams supporting it.
An application team may pursue an AI service to meet an immediate operational need, while security and networking teams work to put the necessary protections in place.
“The security and networking team needs to keep up with that,” he says.
These teams need visibility across AI usage, supported by endpoint controls, firewalls and centralised logging.
Chan calls this “AI observability”, allowing organisations to see which AI services are being used in their environment.
Using AI to detect threats earlier
In his presentation, Chan examined how AI can support cyber defence alongside protecting AI systems.
He described automated responses such as quarantining a compromised device, as well as deploying decoy systems to help defenders observe an attacker’s activity.
Machine learning and AI can also be used to coordinate defence and shorten the time needed to detect and respond to threats, he said on the panel.
He also said Fortinet was using frontier AI models to address vulnerabilities and assist customers to provide better security in their environment.
Chan gives an example of a laptop that usually uploads about one gigabyte of data a day suddenly sending out ten.
That should prompt an investigation for potential data leak, he says. Recognising that change requires the organisation to first understand normal activity.
“In order to detect that, you also need to baseline the traffic,” he says.
Threat intelligence provides another important context when securing systems.
Chan describes tracking malicious domains, web addresses and file hashes associated with attack groups, then incorporating those indicators into security tools.
This can help defenders connect activity on an endpoint with a known threat.
Security data needs to be easier to bring together, he says. Information spread across network, endpoint and authentication systems can make it harder for an AI agent to consolidate what is happening across an organisation.
Cooperation matters beyond the agency’s own systems too.
Chan explains that threat intelligence sharing with government agencies works in both directions, helping vendors and public bodies improve their understanding of emerging threats.
“We may compete commercially, but when it comes to cybersecurity, sharing threat intelligence helps strengthen everyone’s defences,” he says.
For critical infrastructure, that cooperation extends to operational technology providers whose equipment controls pumps, valves and other machinery.
As agencies give AI agents more responsibility, Chan’s emphasis remains on retaining the ability to intervene.
They need to know what an agent can access, monitor how it uses that access and withdraw its authority when something goes wrong.