Beyond backup: Rethinking data infrastructure for the ransomware era
By Synology
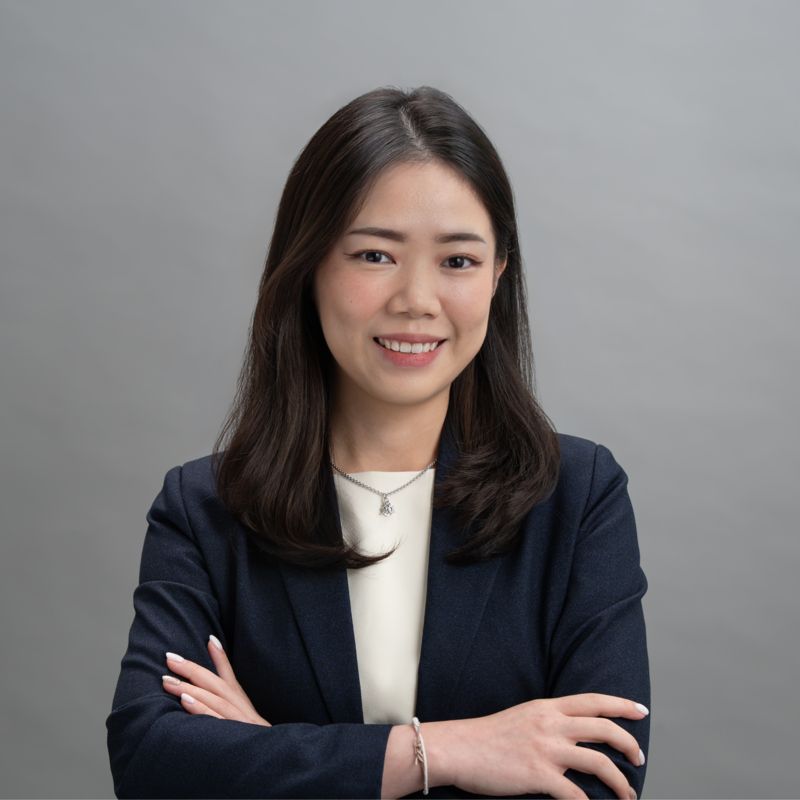
Resilience must be designed and automated into the infrastructure, and cannot be policy document that assumes a human will do the right thing under pressure, says Synology's country manager for Singapore, Emily Oh.
-1789102719147.jpg)
Resilience has to be designed and automated into the infrastructure — it can't be a policy document that assumes a human will do the right thing under pressure. Image: Canva
The backup used to be the safety nets, but now it's being targeted.
According to global cybersecurity company Sophos, backup compromise is now attempted in over 94 per cent of ransomware incidents, and succeeds in 57 per cent of them.
Attackers have also gotten faster, as another cybersecurity company Mandiant's M-Trends 2026 report puts average exploitation at roughly seven days before a patch is even released.
This is much faster than the previous weeks-long headstart that cyber defenders used to have.
Speaking to GovInsider, Synology's country manager for Singapore, Emily Oh, says that this shift means "we have a backup somewhere" has stopped being a resilience strategy.
"It became a hope," she says.
Having a backup isn't the same as recovering
Oh points to three recurring patterns among organisations that assumed they were covered.
- The backup lived on the same network as production systems with no real isolation, so it was encrypted or deleted alongside everything else.
- The backup existed but had never been test-restored, so a corrupted backup only surfaces during the actual incident.
- The backup worked, technically, but far too slowly. When services are expected back within minutes, legacy backup media can take roughly an hour per terabyte to restore and services remain unworkable.
"Having a copy of data and having a verified, fast path back to clean operations are two very different capabilities," she says.
If a backup alone isn't enough, then what is? She highlights four capabilities that need to function together as one system.
These capabilities include immutability, so backup versions cannot be changed or deleted within their retention window, even by compromised admin credentials; isolation, through automated logical air-gapping rather than someone unplugging a drive; continuous verification, so recoverability is proven continuously; and speed, with disk-based recovery that can restore a clean point in time within minutes.
Across these four capabilities, the common thread is that resilience "has to be designed and automated into the infrastructure — it can't be a policy document that assumes a human will do the right thing under pressure."
Where resilience breaks down
According to Salesforce research, organisations typically run close to 900 applications on average, with only around 29 per cent integrated. Fragmentation worsens as data spans more environments.
"Operational data are protected under one policy on-premises, but the same workload running in the cloud isn't held to that same standard," Oh explains.
AWS' published pricing also found that pulling data back out of the cloud can cost four to six times more than storing it there. This locks organisations into whichever posture they set up first.
Oh says that accessibility and protection don't necessarily have to be in tension.
The old model, which is physically disconnecting a drive and shipping tape offsite, did trade convenience for safety since a person had to intervene every time.
Automated, logical isolation removes that trade-off by allowing systems to run scheduled transfer windows and stay disconnected the rest of the time, protected by default and accessible on a predictable schedule, she says.
With role-based access and multi-factor authentication layered on top, legitimate users can move faster while compromised credentials get blocked.
What this means for agencies moving forward
For private companies, downtime is usually measured in revenue and reputation.
For a public agency, it can mean citizens losing access to healthcare, benefits, or other essential services.
In Singapore where government services are increasingly digital and expectations around cybersecurity and availability are high, Oh emphasises that agencies need to prioritise infrastructure based on the criticality and citizen impact of each service.
Resilience needs to also go beyond just having a backup, she says.
Resilience in practice means that agencies need control over sensitive data, protected recovery copies, and regular testing to prove that critical services can be restored.
"Resilience is not just an IT investment," Oh says. "It is part of maintaining continuity of public services and public trust."
For agencies working with legacy systems and constrained budgets, her advice is to start by identifying the most critical workloads for upgrades. These workloads the ones that would halt operations if lost.
"That [also] means being honest about what your current systems can actually prove: can you demonstrate that your most critical backup is recoverable within the time your business needs?"
She adds that many legacy tools cannot answer that since they lack built-in immutability or automated restore verification altogether.
Be it an isolation gap, verification gap or/and a recovery-speed gap, these gaps should guide the first investments.
On what ransomware-"ready" infrastructure looks like three years from now, Oh expects this to increasingly mean continuous rather than periodic.
That is to restore verification running constantly in the background rather than as an annual drill, with recovery measured in minutes as a baseline, not an aspiration.
As AI agents take on more autonomous, high-speed actions inside enterprise systems, infrastructure need to assume some of those actions will go wrong and build in an automatic "undo" that isolates and rolls back before a human even notices.
"The organisations best positioned for that will be the ones already running AI and recovery on infrastructure they control, rather than depending entirely on third parties for both," she says.
Emily Oh will speak on "Build a secure and future-ready data infrastructure" at Synology's Singapore Exchange 2026 event on November 5 at Marriott Tangs Orchard, Grand Ballroom 3, Singapore. You can find out more about the event and register here.