Inside the lab where security teams attack their own code with frontier AI
With cyber attackers using AI to compress weeks of hacking into hours, Philippa Cogswell from Palo Alto Networks' Unit 42 shares what her team learned by turning the same tech on itself, and what public agencies should do next.
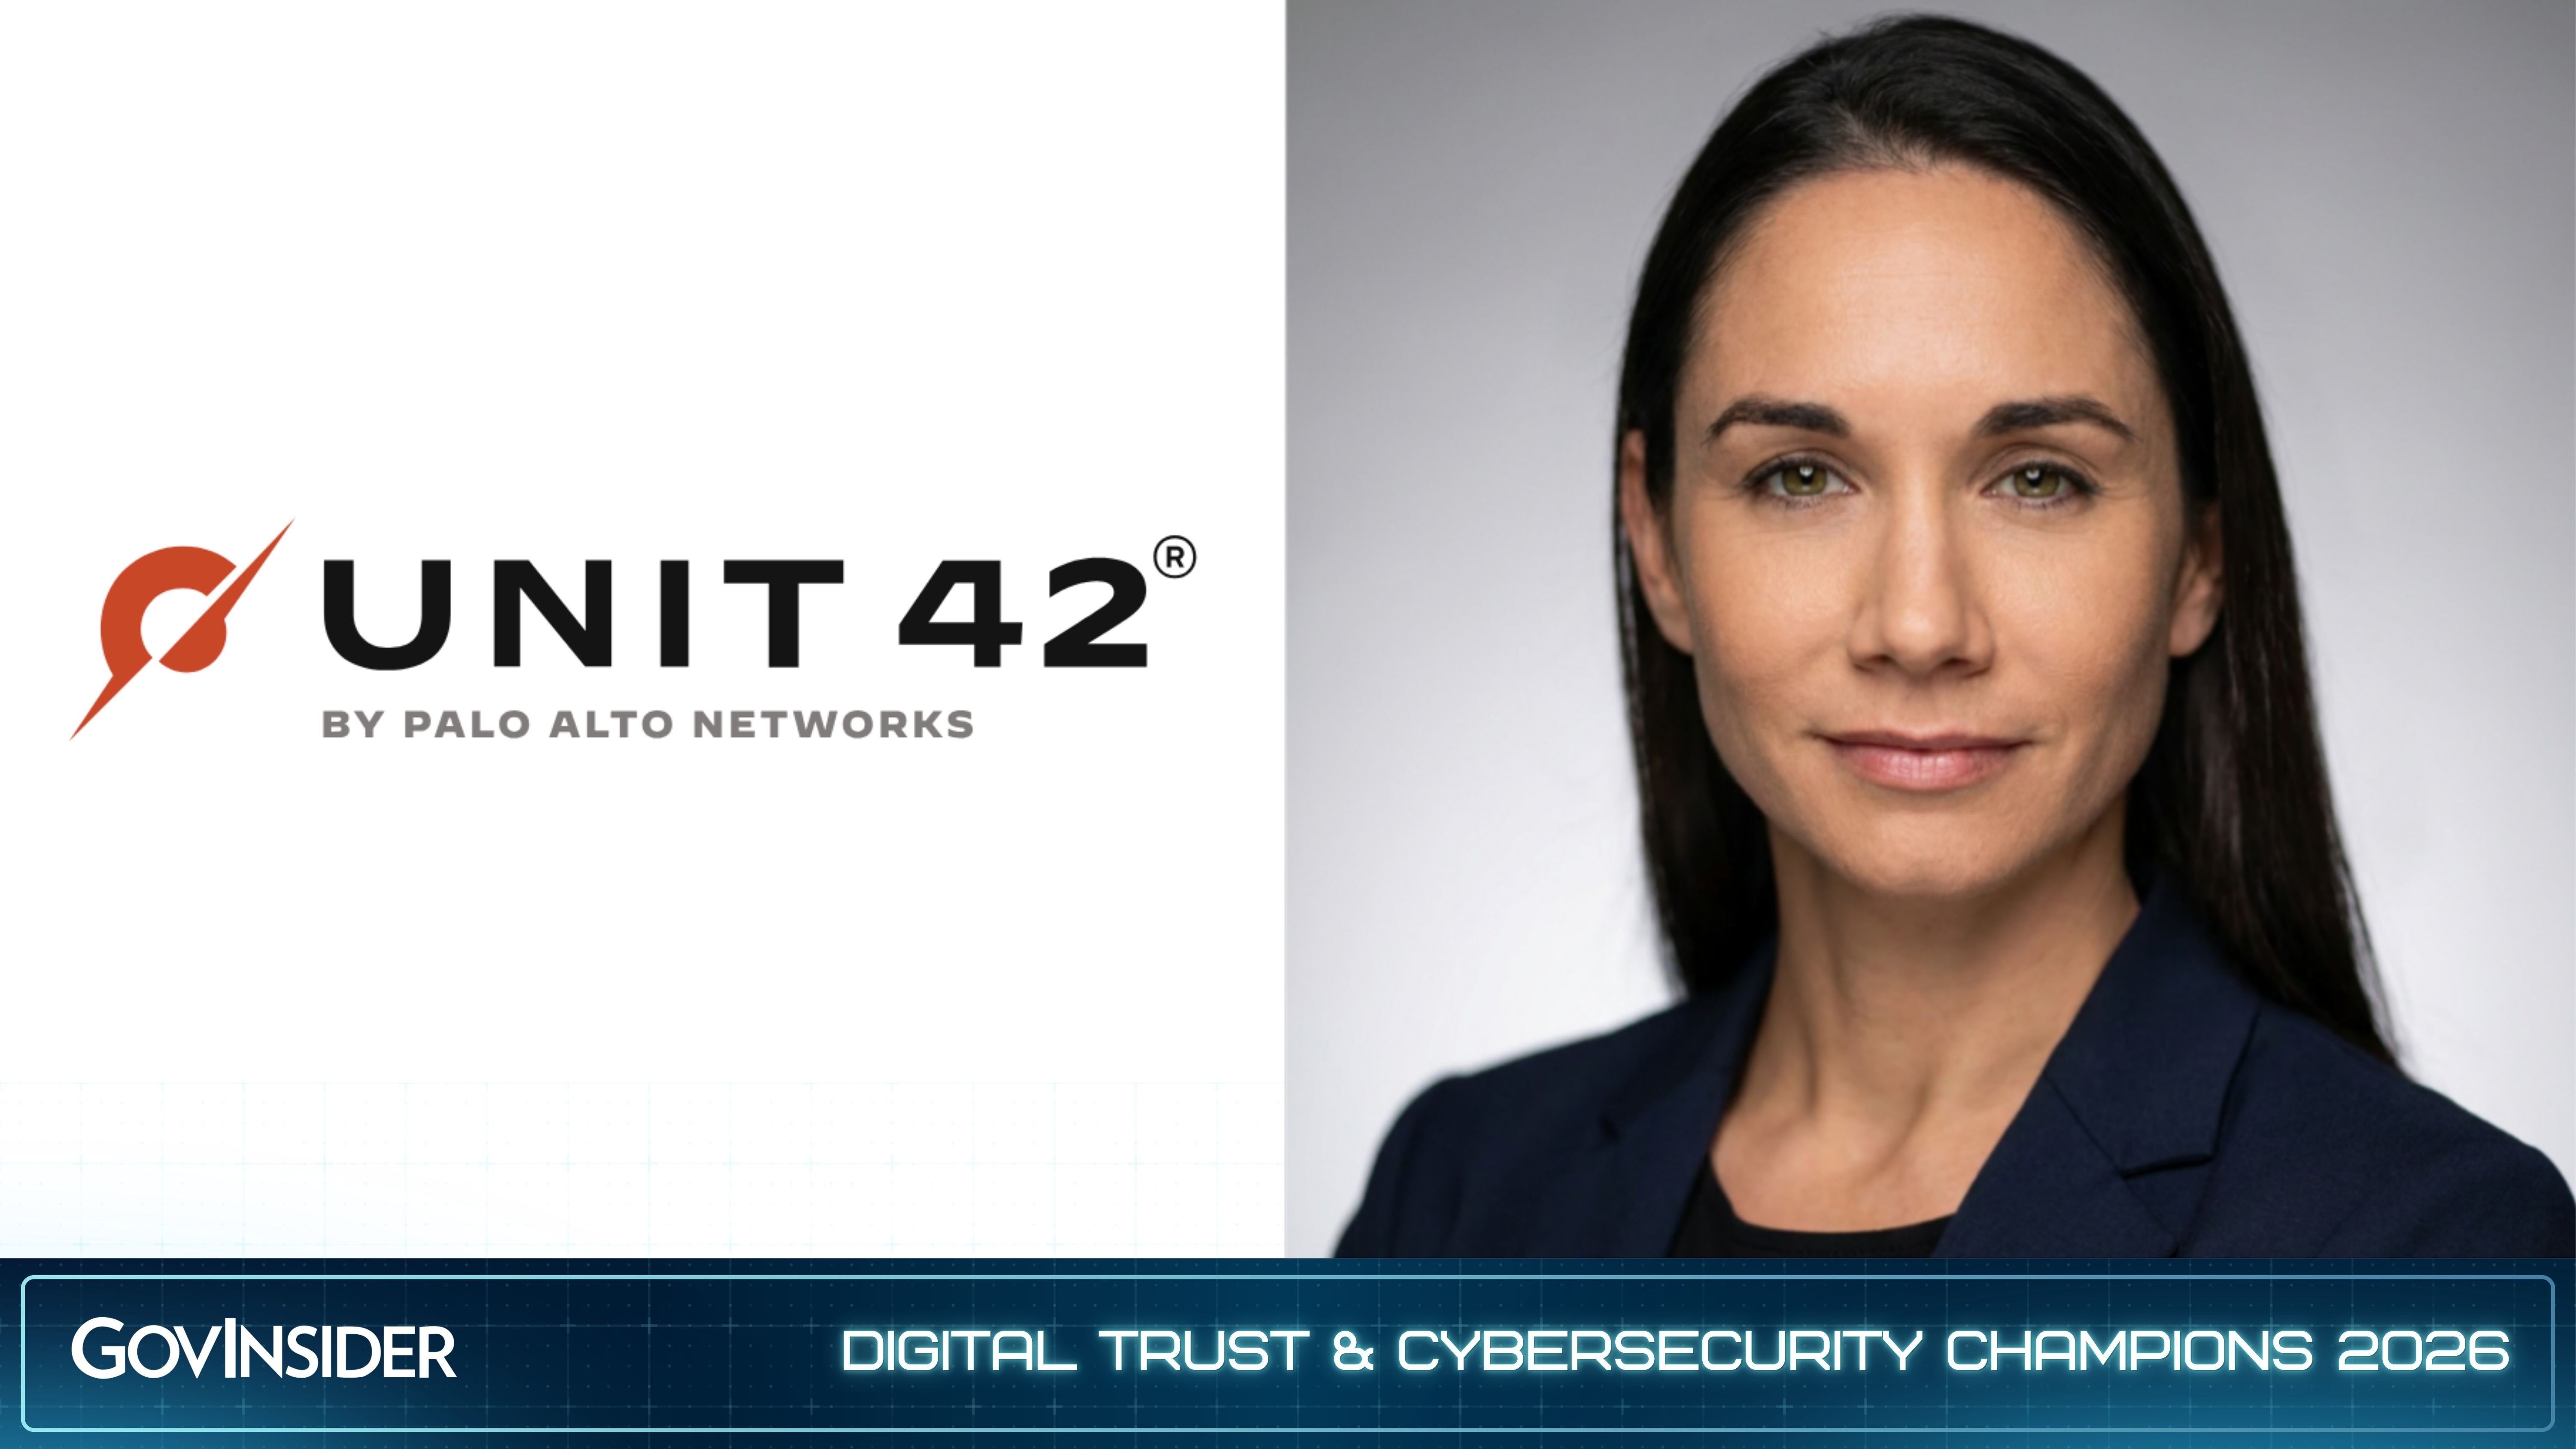
Philippa Cogswell, Vice President and Managing Partner for Unit 42 (Asia-Pacific and Japan) at Palo Alto Networks. Image: Cogswell's LinkedIn
This story is part of GovInsider's Digital Trust & Cybersecurity Champions 2026 Special Report.
Picture a thief, skilled but limited by the hours of the day, picking a door lock by hand.
And now, give that intruder a high-speed master key that can attempt thousands of combinations every minute, working 24/7, without the need to sleep or eat.
Philippa Cogswell, Vice President and Managing Partner for Unit 42 (Asia-Pacific and Japan) at Palo Alto Networks, uses this analogy to describe what frontier artificial intelligence (AI) has handed to cyber attackers today.
She shares with GovInsider about one recent incident her team investigated, where an attacker used AI agents to execute more than 50 hacking techniques in under 10 hours, which would normally take a team of human attackers more than several weeks.
Unit 42 is Palo Alto Networks’ threat research, incident response and cyber consulting team, which investigates cyberattacks, runs AI security research, and advises global governments and organisations.
Using the same capabilities, Cogswell's team is pointing these frontier AI models at its own software to uncover their vulnerabilities, acting as what she calls "Customer Zero."
She shares more about the lessons learnt from these exercises, why even mature organisations carry hidden risk, and what resource-constrained governments should prioritise.
'Customer Zero': Essentially the defender getting the first look
To defend against attackers using frontier AI, Unit 42 first has to understand what the technology can do. Cogswell's team is using that head start to analyse its own code first.
Through early access programmes such as Anthropic’s Project Glasswing and OpenAI’s Trusted Access for Cyber, Cogswell says her team gets “a first look at the art of the possible”, and a sense of “how we might anticipate adversaries will pivot their activities.”
Pointing these models at its own software allows her team to find and fix complex flaws in near-real time and to build protections for customers around the world, she explains.
She notes that in three weeks, the scans delivered a year’s worth of traditional penetration testing results, and found more than three times more critical vulnerabilities per product than legacy methods had found.
Penetration testing and red teaming is the practice of hiring experts to probe a system for weaknesses before attackers do.
"The lesson for government agencies is clear: Defending at human speed is no longer viable.
Organisations must close years of accumulated exposure while securing the AI they are rapidly adopting," she says.
Beyond commercial models, Cogswell highlights another Unit 42 project called Project NOVA, which is an autonomous, AI-driven research framework built to hunt for software flaws.
The framework identified more than 14,000 vulnerabilities across roughly 5,000 open-source projects in under two months.
According to her, reaching 10,000 discoveries at that scale previously took over seven years.
“The sheer volume of hidden risk that AI can surface in minutes is a wake-up call for everyone,” she stresses.
The hidden risk inside mature systems
Even the most mature organisations carry hidden security flaws that manual reviews cannot find, says Cogswell.
According to her, human reviewers tend to hunt for more isolated flaws, while frontier models look at how weaknesses connect.
“We aren’t just looking for single ‘critical’ bugs anymore, we’re looking for how an AI might chain multiple ‘minor’ issues together to create a viable attack path, and potentially catastrophic incident,” she explains.
With a compressed attack timeline and an evolving attack surface, traditional, point-in-time security assessments are no longer enough today, she adds.
Today, Palo Alto Networks use a combination of frontier AI models and human specialists to discover, validate and speed up fixes.
What public agencies should do
Cogswell recommends public agencies to prioritise continuous visibility instead.
Agencies should use frontier AI tools to operate at machine speed, she says, but with “the support of human expertise and threat intelligence” to validate the findings.
The aim is to build tailored fix plans that break the critical attack paths, which are the routes an intruder would take to reach the most sensitive information or critical digital services.
Closing the gap between regulation and AI adoption, she argues, "requires an active co-design partnership."
"Because developers and frontline security practitioners see new capabilities and vulnerabilities first, industry naturally informs the operational playbook," she explains.
Policymakers then bring into law. She notes that across Asia-Pacific, governments are responding by continuously updating legislation, citing South Korea’s AI Basic Act, Singapore’s Model AI Governance playbooks, among others.
She adds that consistency matters, as fragmented rules across the region can “create compliance bottlenecks and security gaps."
The next leap to a successful public-private partnership is to support governments to align new laws with global standards so that businesses can innovate securely across borders, she explains.