Microsegmentation can limit the impact of cyberattacks in the age of AI
By ViewQwest
ViewQwest’s Chief Growth Officer Peter Molloy explains why microsegmentation and faster decision-making are essential to strengthening cyber resilience in the AI era.
Microsegmentation limits how far an attacker can move through a network, so a breach at one point does not spread across the entire system. Image: Canva
When attackers targeted a French supermarket chain, they shut down its refrigeration systems, causing widespread disruption and food waste.
The incident illustrates how a cyberattack on one part of an organisation can affect operations far beyond its initial target.
So how can organisations stop one attack from spreading?
According to ViewQwest's Chief Growth Officer Peter Molloy, the answer lies in limiting how far an attacker can move through a network.
“Microsegmentation would have stopped it. It might have hit Store 1, but it wouldn’t have reached Store 60,” he says.
Microsegmentation divides a network into smaller segments, allowing organisations to restrict which users, systems, and applications can communicate with one another.
If one segment is compromised, this approach prevents an attacker from moving laterally across the wider network.
Molloy argues that although organisations increasingly recognise the “assume breach” principle, which is the idea that attackers will eventually get in, many have yet to translate that understanding into action.
“The only way to create deterministic policies and deploy them at scale, while keeping the business running, is to have microsegmentation in place,” he says.
Organisations also need clear visibility of access rights: who is authorised to access particular systems and data, and which people or artificial intelligence (AI) agents attempt to gain access.
Containing attacks as threats evolve
The urgency is growing as AI models become more capable.
Tasks that previously required repeated prompts and checks can now be completed over hours, with far less human intervention.
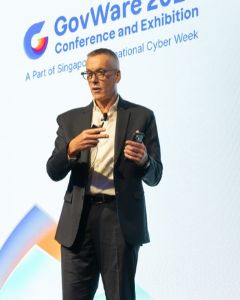
Molloy describes this as a problem of two different clocks.
AI capabilities are advancing quickly, while organisations still make security investment decisions through annual budgeting cycles and lengthy approval processes.
“Instead of looking at the threats you face today, which change weekly, you look back 12 months. That doesn’t make sense to me.”
He notes that while conventional security measures remain necessary, organisations should not assume that upgrading existing technology automatically improves their defences.
The priority is to understand the threats they face now and ensure their security measures address them, he adds.
Microsegmentation supports this approach by limiting the damage an attacker can cause after gaining access.
“If you can contain, and you work on a strong zero-trust basis where you break the connection between authorised access and everything else, you buy time to respond,” Molloy says.
Faster decisions, with clear boundaries
Molloy emphasises that technology alone cannot solve the problem if internal decision-making remains too slow.
Organisations need to reconsider the processes that stand between identifying a threat and acting on it.
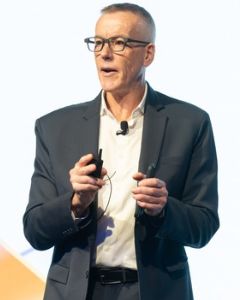
“You have an enemy outside the perimeter operating at light speed, while your own path from idea to implementation takes multiple committees and weeks. We don’t have that luxury anymore.”
This means that organisations should classify their assets and determine which decisions can safely be automated.
He recalls meeting a chief information officer whose managed detection and response provider repeatedly asked for instructions before acting on potential threats.
The approval process introduced a delay of two or three hours.
The CIO would rather have the provider block a threat automatically under agreed conditions, even if that meant temporarily losing access to one service.
The alternative was losing the entire infrastructure for two days, which would be far more damaging.
“Once you understand your application infrastructure, you can decide when a human sits on the loop rather than in it at every step,” he says.
The challenge for organisations is therefore to define clear rules in advance: which actions can be taken automatically, what risks are acceptable, and when a human must intervene.
Governing AI use before it spreads
Alongside traditional cyber threats, Molloy identifies shadow AI as an increasingly pressing concern.
Just as employees once adopted unauthorised IT services, they are now using AI tools without necessarily following organisational policies.
“Now individuals spin up their own AI because no controls exist to stop them,” he says, citing an IBM report that 97 per cent of organisations breached over the preceding 12 months had no control over which AI tools were being used in their environments.
According to him, organisations need to establish which AI models employees may use, the parameters governing their use, and the projects in which they can be deployed.
They must also be able to restrict access when necessary.
The controls for AI agents need to go beyond general guidelines.
Organisations should establish deterministic policies that specify what an agent is authorised to do and how its behaviour will be assessed.
Amid the growing role of automation, Molloy says people remain critical to effective AI adoption.
The value of human-machine collaboration lies not simply in carrying out tasks, but in also understanding the processes being automated and recognising what a good outcome should look like.
“If you don’t understand what good and bad looks like, AI can send you down a rabbit hole very quickly,” he says.
As AI capabilities continue to advance, organisations may not be able to prevent every attack.
But by limiting how far an attacker can move, automating decisions within clearly defined boundaries and retaining meaningful human oversight, they can improve their ability to contain an incident before it becomes a wider crisis, he concludes.